Security
Built to hold as little as possible.
ARX puts your company’s AI Operating System on each employee’s computer. The model runs under your account, your systems stay the systems of record, and Imperium keeps the smallest footprint that still lets us serve you.
Protection by design
Nothing of yours to steal
Imperium never holds your passwords or sign-in tokens for the apps ARX connects to. Each person grants access from their own browser and can withdraw it in one click; your administrator can withdraw everyone's at once.
Your systems stay the system of record
When ARX reads from or writes to your accounting, email, calendar or CRM, it does so at the moment of use. We do not copy or warehouse the contents of those systems.
Money never moves without a person
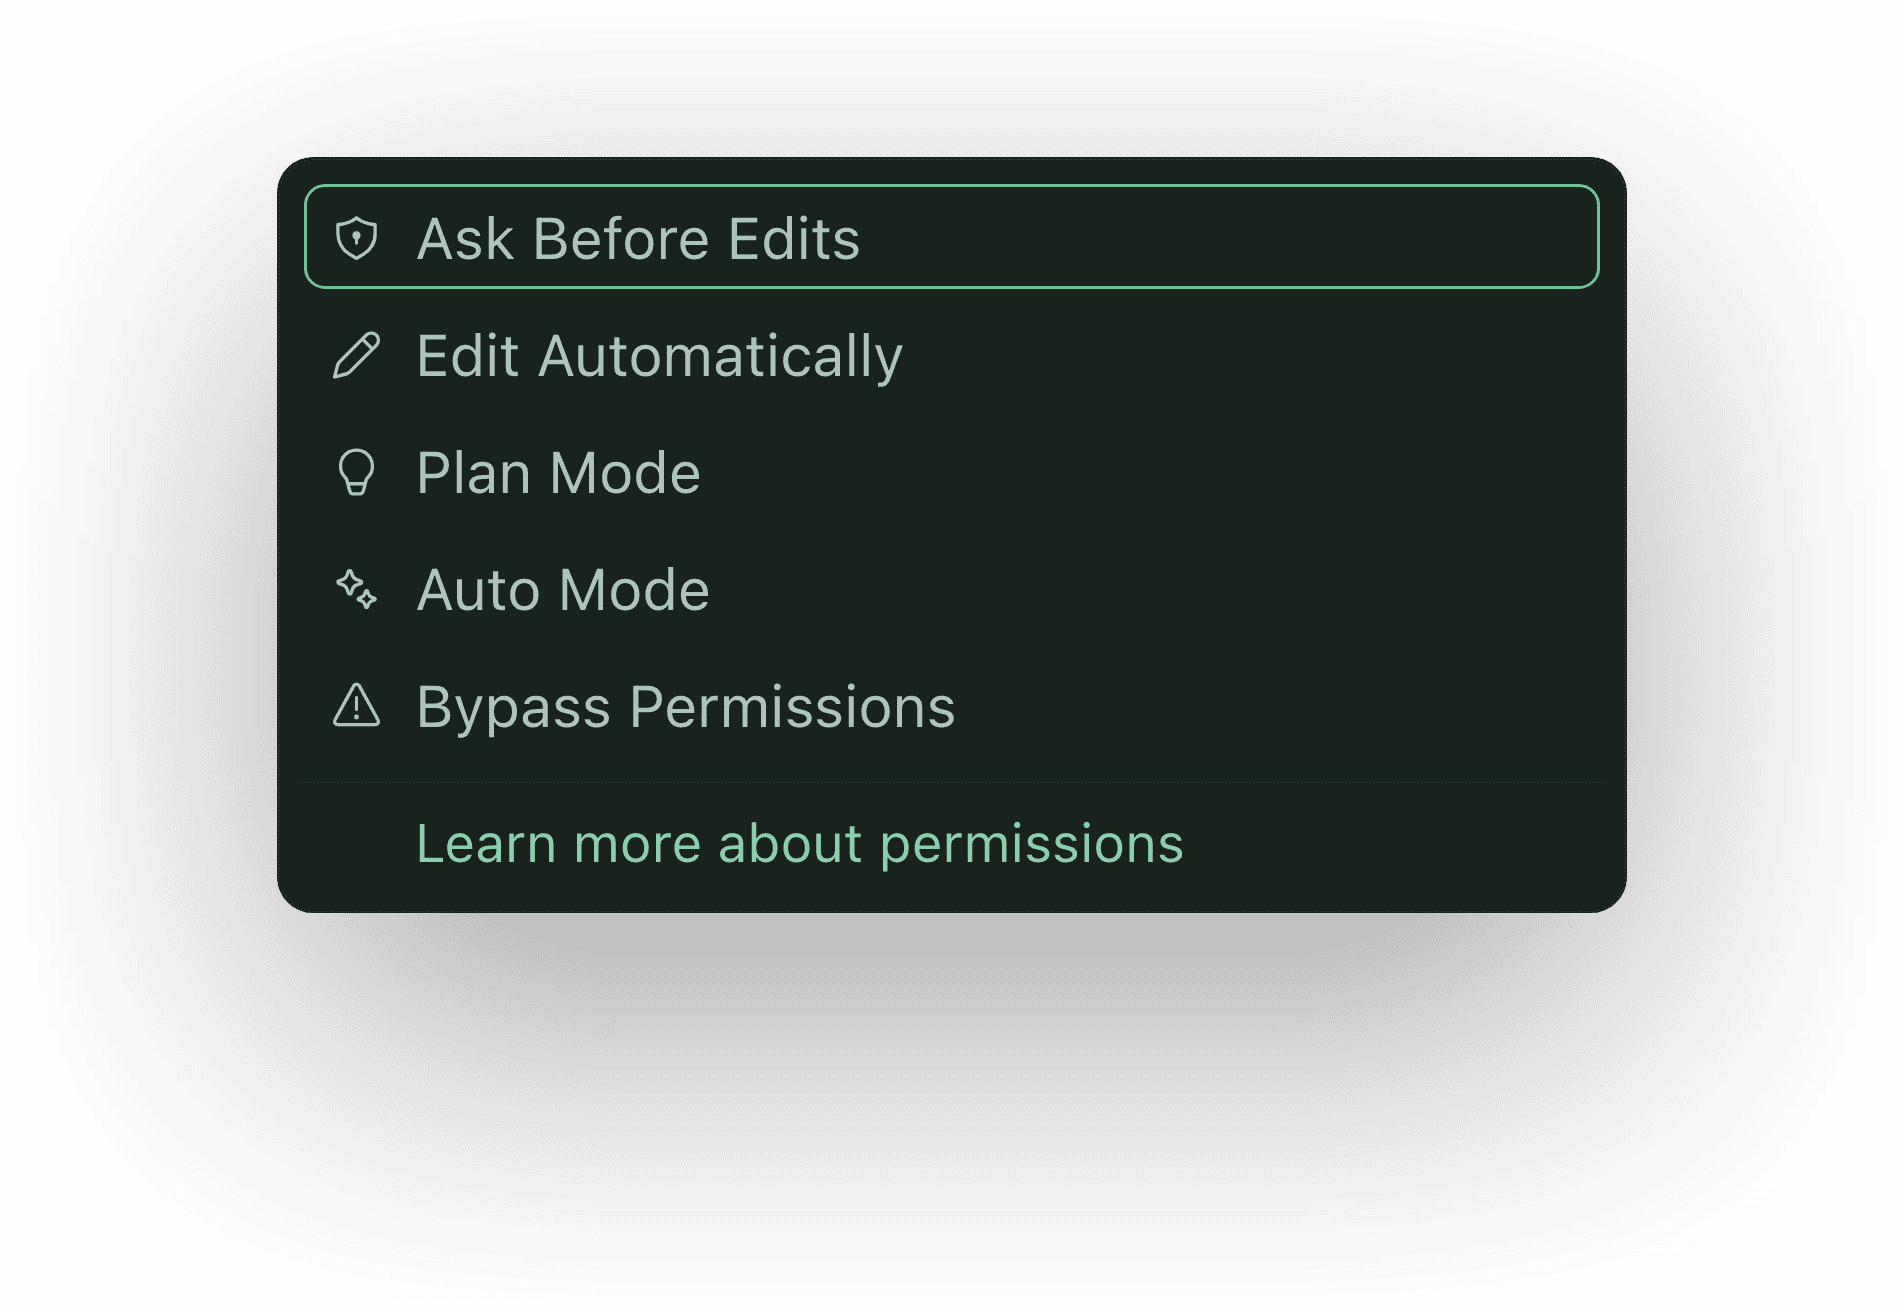
Financial actions are draft-only by design. Nothing posts to your ledger, pays a bill or sends an invoice until a person approves it in your own system.
Least privilege, per role
Each person’s OS gets only the tools their role allows. Policy is enforced on our side and again on the device, and takes effect within a minute of a change.
An audit trail, not a data trail
Every action against a connected system records who, what, when and whether it succeeded. It never records the arguments or the data returned.
Verified software on every machine
Updates and the AI engine are cryptographically hash-verified before they install, and macOS builds are signed and notarized. The assistant cannot modify the application it runs in.
Independent assurance, stated plainly
We are a small company selling to large ones, so we would rather show you exactly where we are than a wall of badges. Ask us for the current scope and available documentation for each programme.
Independent code audit completed September 2026. Contact us for available findings, remediation status and planned testing.
Answers your security team will ask for
How it's built
Keep up with how it is built.
Security notes in the newsletter: what changed in the controls, new attestations as they land, and what each audit found.
News
- DocumentaryHow a property developer avoided ten hires in sixty days12 min · Sixty days inside GeoNet, a developer with three brands going construction ready at once, as the AI Operating System goes in across the whole team.Watch
- Blog · 19 August 2026Built to hold as little as possible6 min readRead more
- Blog · 26 August 2026Controls you can see5 min readRead more
- ProductARX, the desktop for the AI Operating System.What the software is, what it holds, and what it never does without a human yes.Read more